Zero Trust Conceptual Architecture
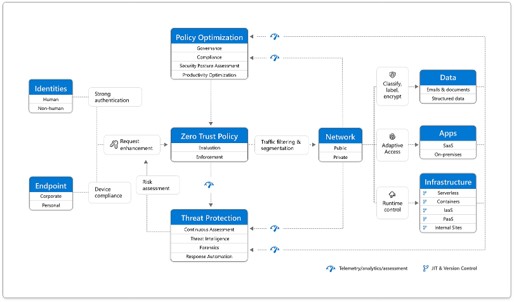
Zero Trust Conceptual Architecture
Zero trust conceptual architecture views security controls as an identity- and policy-driven model rather than a network perimeter model.
Core Components
- Users
- Devices
- Infrastructure
- Applications
- Identity services
- Policy enforcement points
- Access decision engines
- Security monitoring
Design Intent
The architecture ensures that access decisions are based on user identity, device posture, context, and application-level policy rather than location alone.
Source
The slide references the Microsoft Zero Trust model and modern security architecture patterns.