
DNS Security / DNSSEC
The goal of DNS security is to create a trusted DNS system by combining DNS data with cryptographic signatures.
A zone owner signs the data in the zone using a private key. Consumers can verify the authenticity of the DNS data using the corresponding public key.
To support signing and verification, DNSSEC adds several record types:
- RRSIG Record – Stores digital signatures for a set of DNS records.
- DNSKEY Record – Stores the public key used for verification.
- DS Record – Stores the hash of the DNSKEY record for delegation.
- NSEC and NSEC3 Records – Explicitly prove that a DNS record does not exist.
- CDNSKEY and CDS Records – Used by a child zone to update its DS record in the parent zone.
Each DNS zone typically has two key pairs:
- Zone Signing Key (ZSK)
- Key Signing Key (KSK)
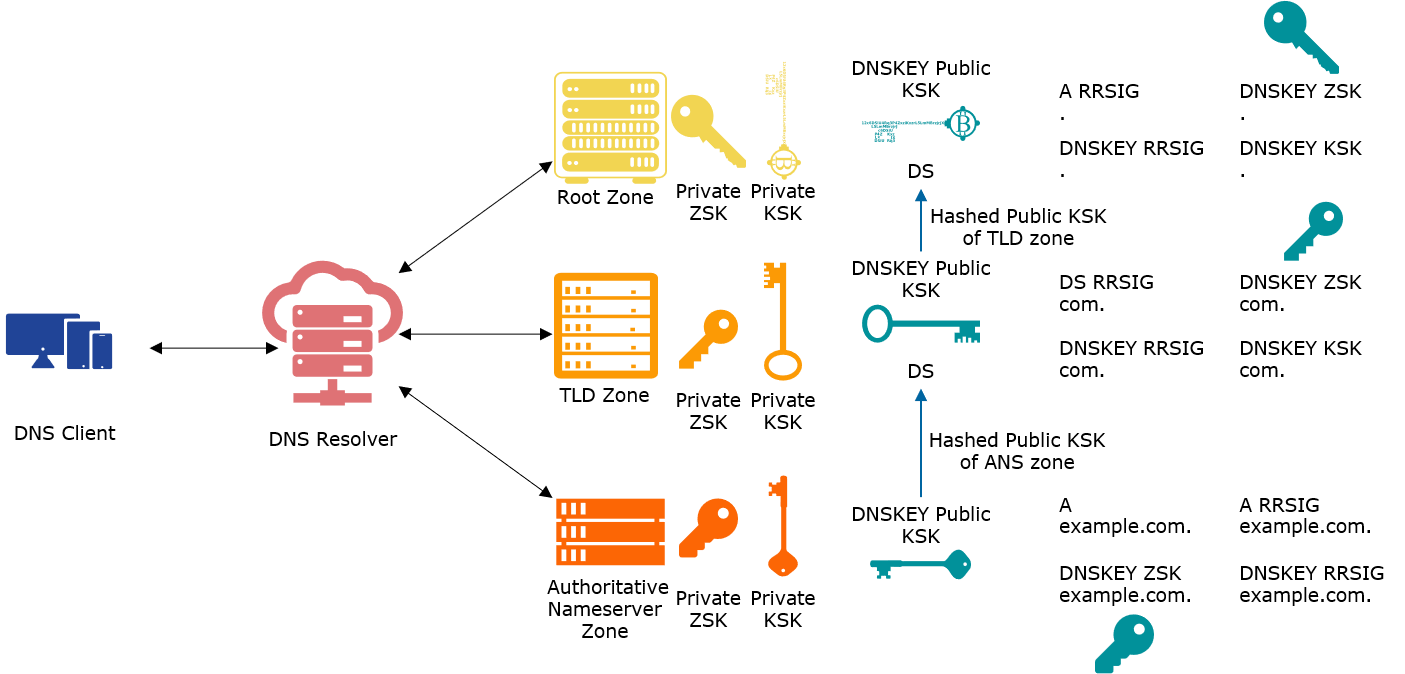
The zone owner signs a set of resource records using the zone signing private key. The public part of the zone signing key is published in the DNSKEY record so resolvers can retrieve it and validate the authenticity of the DNS data.