Cloud Core Connectivity Security
Cloud Core Connectivity Security
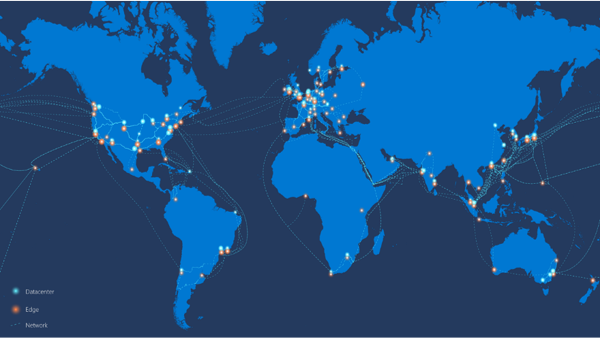
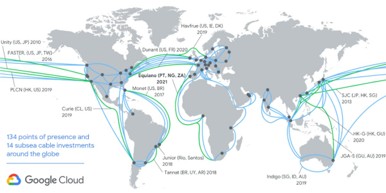
Cloud providers operate vast private networks and dedicated backbone connectivity. Data centers, edge locations, and regions are interconnected by global fibre and subsea cable networks, so most cloud traffic travels over provider-controlled links rather than the public internet.
Why Connectivity Needs Protection
Even with a private backbone, internal and external traffic paths must be secured against interception, tampering, and denial of service. Physical fibre routes, interconnect points, and edge locations are part of the attack surface.
Security Controls
- Firewalls and gateways
- Proxies
- Intrusion detection and prevention systems (IDS/IPS)
- Honeypots and deception technologies
- VPN and encryption of traffic in transit
- Authentication and authorization
- DDoS protection
- Continuous improvement of platform protections
Overall Goal
Core connectivity security ensures that traffic between customers, edge locations, and cloud regions stays confidential, intact, and available, combining network controls, detection capabilities, and strong governance.