Cloud Management Plane and API Security
Cloud Management Plane and API Security
The management plane is the set of consoles, APIs, and tools used to create, configure, and administer cloud resources. Because it controls everything in the environment, compromise of the management plane is far more damaging than compromise of a single workload.
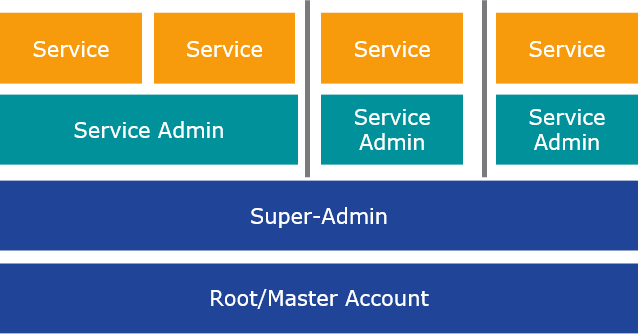
Administrative Hierarchy
- Root/master account: the most privileged identity, with unrestricted control of the cloud account.
- Super-admin: administrators who manage the account-wide configuration and delegate access.
- Service admin: administrators scoped to individual services or workloads.
- Services: the resources and applications consumed by users.
Key Risks
- Compromised or shared root credentials
- Excessive administrative privileges
- Unprotected or poorly authenticated APIs
- Unmonitored configuration changes
Recommended Controls
- Protect the root account with strong multi-factor authentication and avoid using it for daily work
- Apply least privilege and separation of duties between admin tiers
- Authenticate and authorize every API call, and use short-lived credentials
- Log and monitor all management plane and API activity
- Restrict management access by network location, device, and context
Security Objective
Limit who can administer the cloud, ensure every administrative action is authenticated, authorized, and auditable, and contain the impact of any compromised administrator.